GDPR Compliance
GDPR COMPLIANCE
Data protection becomes a continuous process, not a one-off project.
An integrated monitoring and control system for the organization's compliance with Regulation (EU) 2016/679, supported by audit, consulting and specialized assistance.
Data protection becomes a continuous process, not a one-off project.
The Mobius solution brings together the assessment of the organization, documentation of measures, responsibilities and compliance monitoring in a corporate governance system.
Data, workflows, systems, premises and contracts are analyzed together so that the measures applied can be tracked and demonstrated.
Questions answered within a coherent framework.
The MOBIUS GDPR solution turns the questions of management, the data protection officer and IT teams into documented and verifiable measures.
From inventorying data to permanent compliance control.
The organization receives coordinated tools and services for each dimension of data protection.
Information audit
Identifying personal data and inventorying the workflows in which it is used.
IT audit
Assessing the information systems that collect, process, transmit or store data.
Physical security
Analysis of the premises, access and physical measures relevant to information protection.
Risk analysis
Identifying vulnerabilities and establishing the measures needed to reduce risks.
Compliance plan
Organizing the measures, priorities, owners and implementation deadlines.
Procedures and records
Drafting and managing the working documents needed to demonstrate compliance.
DPO assistance
Specialized support for the data protection officer and day-to-day activity.
Training and control
Staff training, planned checks and keeping a history of actions.
Assessment, implementation and monitoring in a verifiable loop.
Compliance is maintained through periodic reassessment and adapting measures to changes in the organization.
Inventory
data and workflows
Assessment
audit and risks
Planning
measures and owners
Implementation
procedures and training
Monitoring
control and updating
Four work streams, a single picture of compliance
Each stream produces records and measures that can be tracked over timeAdministrative, legal and technical work within the same framework.
Compliance requires coordination between management, the data protection officer and legal, IT and security specialists.
Identify
Locate personal data and the processes that use it.
Assess
Analyze compliance, security and associated risks.
Correct
Apply the established administrative, legal and technical measures.
Train
Prepare staff and record training activity.
Control
Periodically check the measures and keep the compliance history.
Compliance can be demonstrated when data, measures and responsibilities are documented.
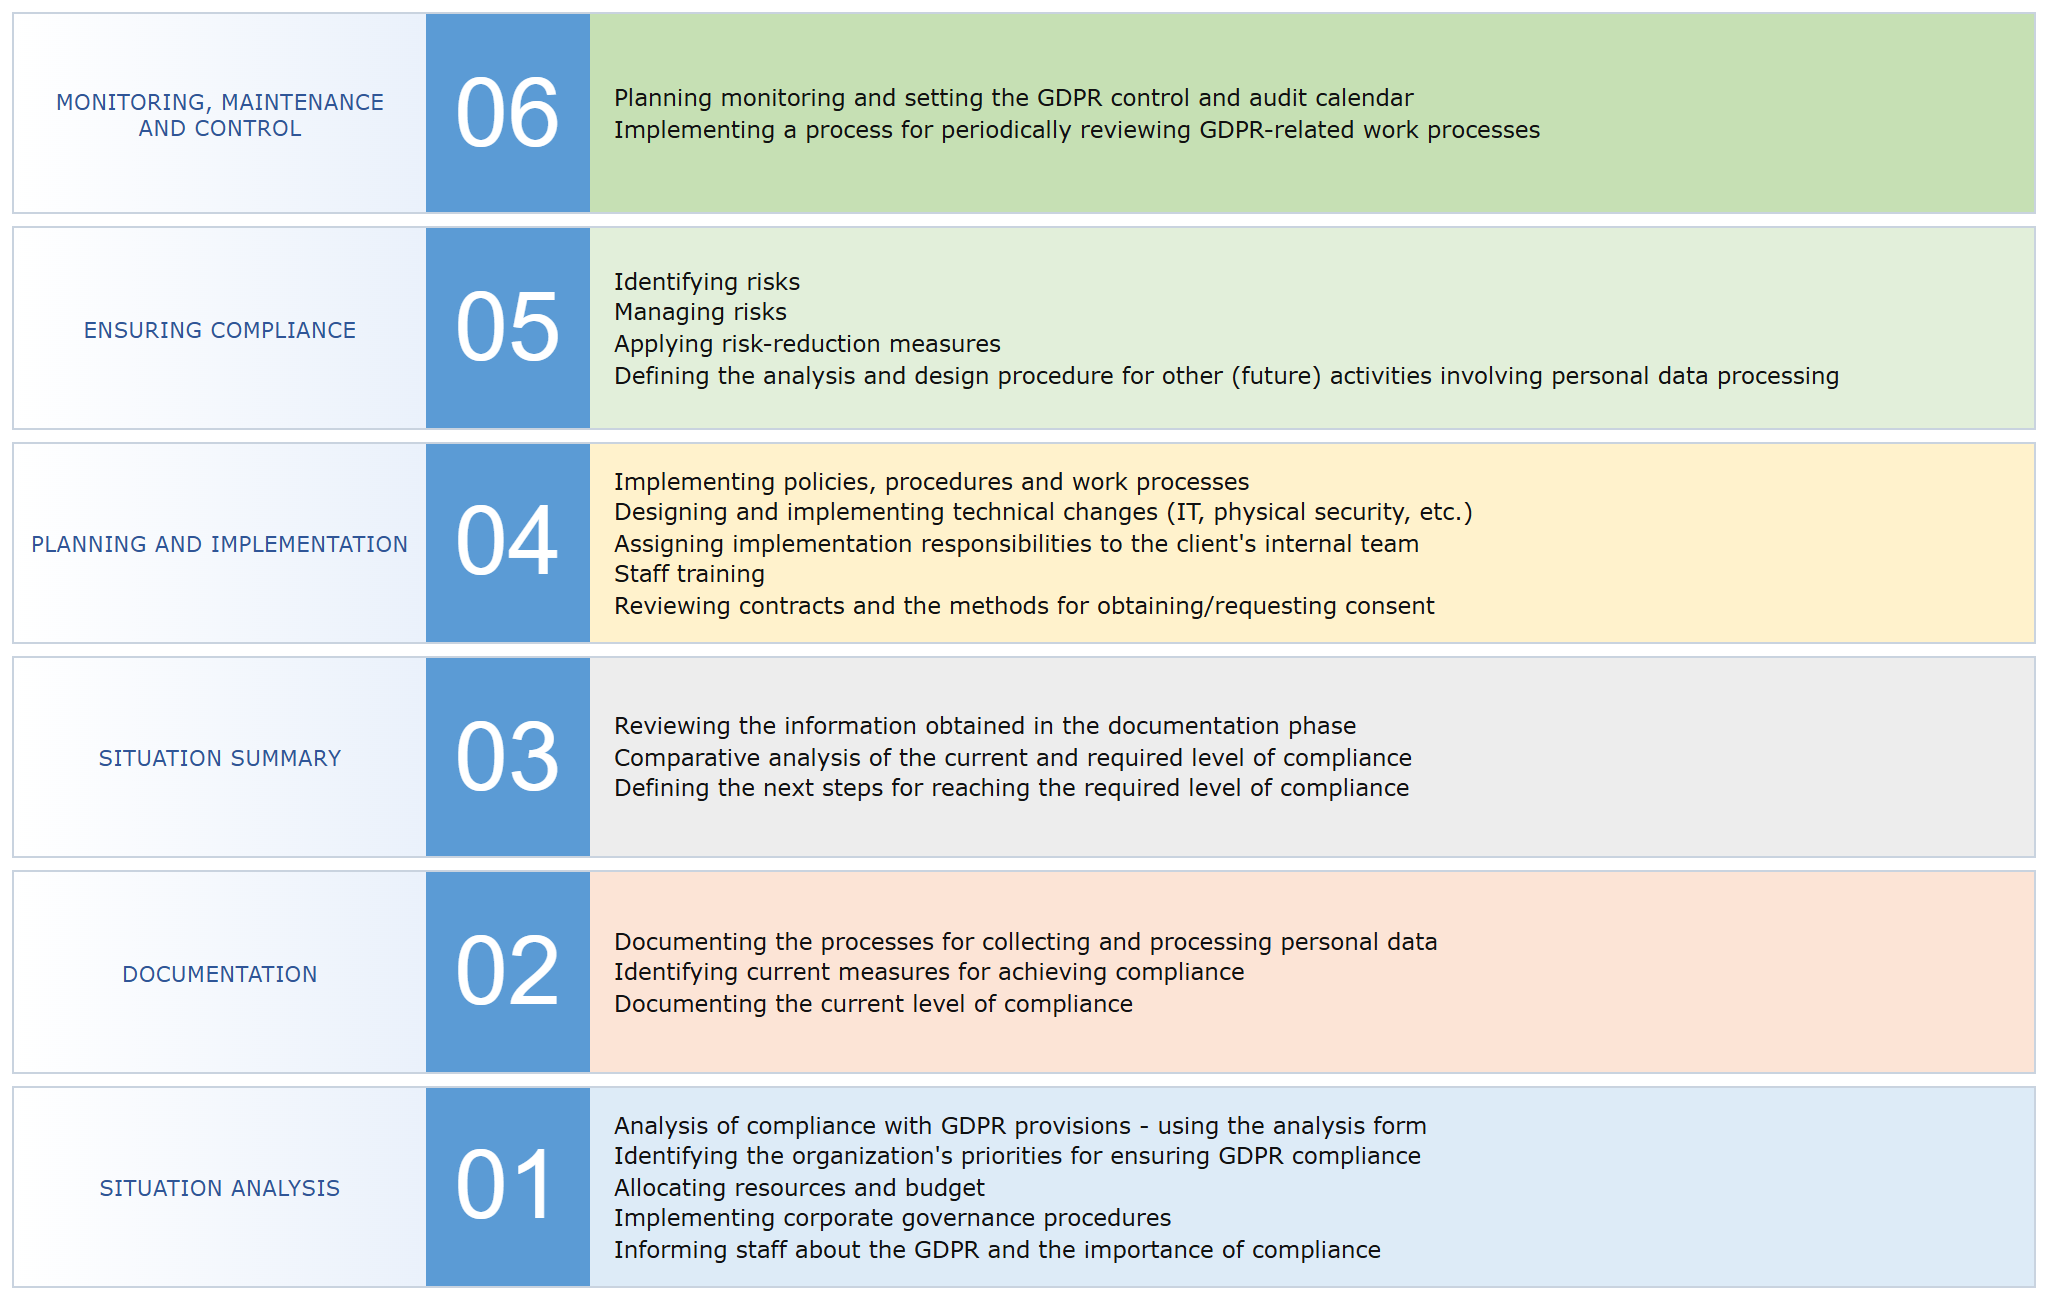
A 6-step compliance path, from analysis to permanent control.
The official Mobius infographic summarizes the compliance stages and the essential responsibilities of personal data protection.

Compliance built around the European Regulation.
The assessment and measures address the applicable data protection obligations and the relevant information security criteria.
Data protection for organizations with complex processes and responsibilities.
Public sector and utilities
Authorities, institutions and providers of energy, water, gas, transport or communications.
Health and financial services
Hospitals, clinics, pharmacies, insurance, banks, leasing and pension administration.
Commerce and technology
Retail, e-commerce, distribution, software, hosting and security services.
Integration in the MOBIUS solutions ecosystem
Assess compliance and turn data protection into a controlled process.
Talk to the Mobius team about your organization's data, systems and processes, from the initial assessment to permanent compliance monitoring.
Request a presentation or a GDPR compliance analysis
Fill in the form and your request is sent directly from the site to the Mobius Software team.